
Your ISO 27001 Certificate Covers Less of NESA Than You Think, and the Gap Is Where the Risk Lives
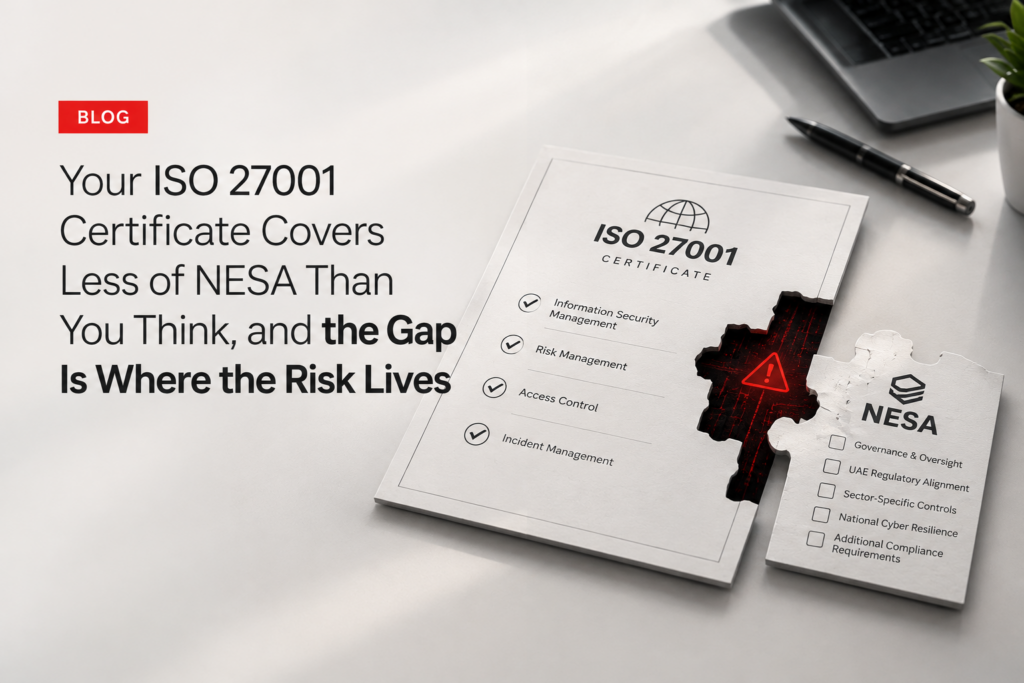
There is a comfortable assumption in a lot of UAE boardrooms: we hold ISO 27001, so our cybersecurity is handled. It is an understandable belief. ISO 27001 is a serious, globally respected standard, and earning it takes real effort. But in the UAE’s current regulatory environment, that certificate covers less ground than most organisations assume, […]